EU Cyber Resilience Act Changes Cybersecurity Rules for Physical Security Systems
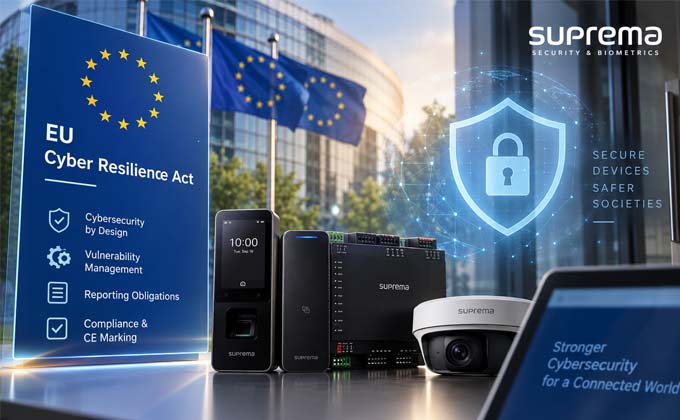
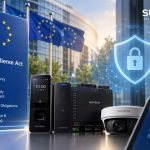
Suprema has highlighted the importance of the EU Cyber Resilience Act (CRA) for the physical security industry, particularly for connected access control systems, biometric readers, and intelligent controllers, as new obligations under the regulation begin to take effect. Regulation (EU) 2024/2847 requires manufacturers to build cybersecurity into products from the design and development stages and to manage vulnerabilities and security updates throughout the entire support period.
Reporting obligations for actively exploited vulnerabilities and severe security incidents began to apply on September 11, 2026, while the CRA will become fully applicable on December 11, 2027, including requirements related to CE marking, technical documentation, and essential cybersecurity requirements. The regulation is particularly relevant to the physical security industry as biometric terminals, door controllers, and access management platforms are increasingly connected directly to corporate LANs or cloud environments. An inadequately protected connected device can therefore become an entry point for attacks on broader IT infrastructure, with the CRA shifting the focus from one-time compliance checks to continuous cybersecurity management throughout the product lifecycle.
The new framework also affects system integrators, distributors, and buyers in the European market, increasing the importance of using hardware and software that meet the required cybersecurity standards. Suprema says it is preparing for CRA compliance by strengthening the cybersecurity of its products and its vulnerability management processes throughout their lifecycle.
In line with the new regulatory framework, the company has also established a dedicated reporting channel at SPOC@supremainc.com for reporting suspected security vulnerabilities or incidents involving Suprema products.