Hackers Exploit Critical Vulnerability in Cisco Expressway
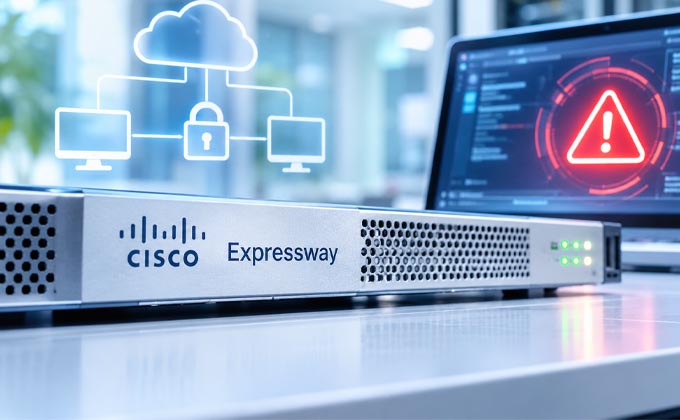
A critical vulnerability in Cisco Expressway was exploited in a cyberattack against an organization in Russia, allowing attackers to compromise four devices and attempt to gain further access to the internal network. According to research conducted by cybersecurity company F6, the attack took place shortly after exploit code for CVE-2026-76466 became publicly available, with the vulnerability receiving a severity score of 9.8 out of 10 on the CVSS scale.
The flaw allows unauthenticated remote attackers to execute commands with the highest administrative privileges on vulnerable Cisco Expressway Core and Edge devices operating in a cluster. The attackers initially gained control of two internet-facing devices before compromising two additional systems within the organization’s internal network. They subsequently used custom Python scripts to scan network resources, access SQL Server and WinRM services, and search for sensitive information in GitLab repositories, with code analysis suggesting the possible use of AI tools.
Cisco released a security patch on October 21 as part of Expressway version X15.5.20, while customers running older X14 releases must upgrade to a supported software version. The US Cybersecurity and Infrastructure Security Agency (CISA) has since added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalog, further emphasizing the need for urgent updates and checks for potential system compromise.